

Saner Container Orchestration Posture Anomaly (COPA)
See and Investigate Configuration Anomalies across Kubernetes and remediate actionable issues
Saner COPA brings detected and remediated anomalies into one view, with resource context, exception management, and a direct path to fixes with integrated remediation

How it works
Powered by Prevention & USI
Saner COPA is part of Saner COSP, bringing SecPod’s prevention-first security approach to Kubernetes posture management and orchestration across on-premises and managed Kubernetes environments.
How it works
Powered by Prevention & USI
Saner COPA is part of Saner COSP, bringing SecPod’s prevention-first security approach to Kubernetes posture management and orchestration across on-premises and managed Kubernetes environments.
Your first 30 days with Saner
From deployment to measurable risk reduction — here is what to expect.

Kubernetes posture anomalies become visible
Saner COPA brings detected and remediated anomalies across Kubernetes clusters and resources into one view. Teams can see which conditions require attention and establish a clear starting point for investigation.
Anomaly reviews become more focused
Teams investigate affected resources and whitelist specific rules or resources when findings do not apply. Removing non-applicable findings creates a more relevant queue for review and corrective action.
Anomaly management becomes repeatable
Investigation, whitelisting, follow-up, and CORM-connected remediation become part of a consistent operating process. Teams retain visibility into unresolved anomalies while maintaining a defined path from detection to corrective action.
Key Features
Everything you need to stay ahead of threats.
Configuration anomaly visibility
See which configuration anomalies still require attention.
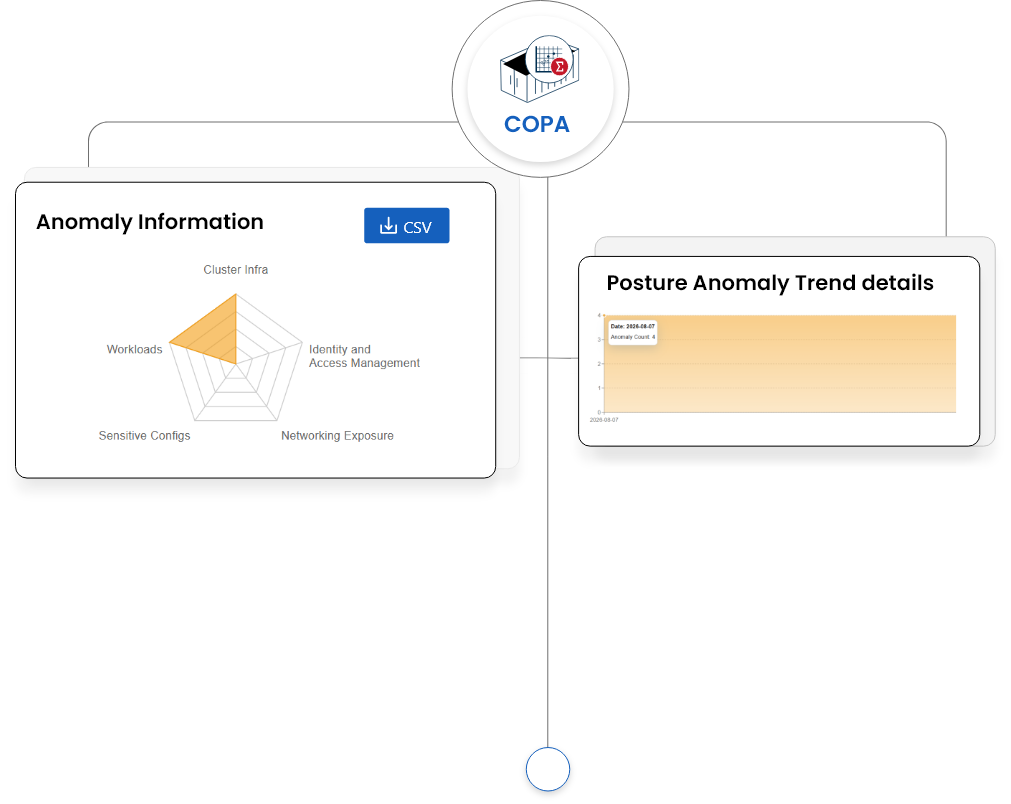
Saner COPA detects configuration anomalies across Kubernetes clusters and resources and gives you a consolidated view. Security teams can see which anomalies remain open and which have already been addressed without treating every assessment as an isolated snapshot. COPA also prioritizes anomalies based on criticality for teams to get a clearer basis for investigation and follow-up.
Anomaly investigation and status context
Understand the state of an anomaly before deciding what happens next.
Saner COPA provides context around configuration anomalies affecting Kubernetes clusters and resources. Detected and remediated conditions remain visible together, while status information helps teams determine whether an anomaly still requires investigation. Security teams can then decide whether corrective action is needed or whether the associated rule or resource does not apply and should be whitelisted.
Rule and resource whitelisting
Exclude non-applicable anomalies from continued review.
Not every anomaly associated with a rule or resource requires remediation. Saner COPA allows teams to whitelist specific rules or resources when the associated condition does not apply. Whitelisted anomalies are excluded from security scans and patching recommendations, helping teams keep their attention on security gaps that still require action.
Fully and natively connected remediation
Move identified anomalies from investigation into corrective action.
Saner COPA connects identified anomalies with remediation through Saner CORM. Teams can initiate remediation at the individual resource level or across identified security gaps, reducing the separation between investigation and corrective action. CORM provides the remediation workflow while COPA retains its focus on identifying, investigating, and managing posture anomalies.
Anomaly trend visibility
Track how posture anomalies change over time.
Anomaly management requires visibility beyond a single assessment. Saner COPA includes anomaly trend views that help teams follow changes in posture anomalies over time alongside the current state of detected conditions. Trend visibility gives security teams additional context when reviewing whether anomalies continue to persist across changing Kubernetes resources and environments.